Get the Book

The CISO Crucible

A Novel of Security Leadership Under Fire

New CISO. Inherited disaster. 90 days to prove it was worth it.

A burned-out security team. A board that sees cybersecurity as a cost center. A breach lurking in the shadows. William Sterling thought he was walking into a turnaround story. He was walking into a crucible.

The 90-Day Journey

Every new CISO faces the same arc. William Sterling lives it in real time.

N
✕✕✕✕
Days 1–30

Get the Lay of the Land

Inherited risks, team dynamics, and the political landscape — plus the crises that won't wait for your plan to be ready.

Days 31–60

Build the Foundation

Frameworks, partnerships, and the hard lesson that the same security message needs different delivery for different audiences.

Days 61–90

Validate and Gain Momentum

Distributed ownership, security as a business enabler, and proving the program works when it's tested under real pressure.

Day 90

Full Circle

Not a victory lap. Not a defeat. Something harder to earn: clarity about what the job actually is.

Every New CISO Knows This Feeling

  • You inherited someone else’s security debt

    Legacy systems nobody documented. Compliance gaps nobody budgeted for. And a cybersecurity team that’s been burned by the last CISO.

  • The board sees security as a cost center

    Every conversation is a budget fight. You know the risk is real—but translating cybersecurity risk into business language feels impossible.

  • Your security team is burning out

    The people holding your incident response together are one bad week from breaking. CISO burnout is real—and it starts with your team.

What Security Leaders Walk Away With

  • A framework for board communication

    The same security message, delivered differently to every audience. Learn why the CFO needs risk metrics, the board needs business narratives, and your team needs transparency.

  • A playbook for cybersecurity leadership politics

    How to build influence without authority. When to protect someone instead of exposing them. Why grace creates more loyalty than leverage—even in incident response.

  • A model for security teams that don’t need heroes

    Security programs that depend on one person are one resignation away from collapse. See what sustainable cybersecurity leadership looks like when the system works without you.

Free Resources for Security Leaders

  • Starting a Security Program — Free Checklist

    New to security programs? Three milestones to get one off the ground. No email needed.

    Download Free — no email

  • The New CISO Field Guide

    The full 90-day playbook as a PDF: Get the Lay of the Land, Build the Foundation, Validate and Gain Momentum — including the Security Champion Program.

    Get the Field Guide

  • Read Chapter 1 Free

    Meet William Sterling on his first morning as CISO of BigCo, and watch his 90-day plan meet reality.

    Read Chapter 1

Read Chapter 1 Free

Optimistic Arrival

William Sterling steps off the subway on a Monday morning, ready to begin his new role as CISO of BigCo. He’s done his research, prepared his 90-day plan, and convinced himself this time will be different. The plan doesn’t survive the first day.
Read Chapter 1

About the Author

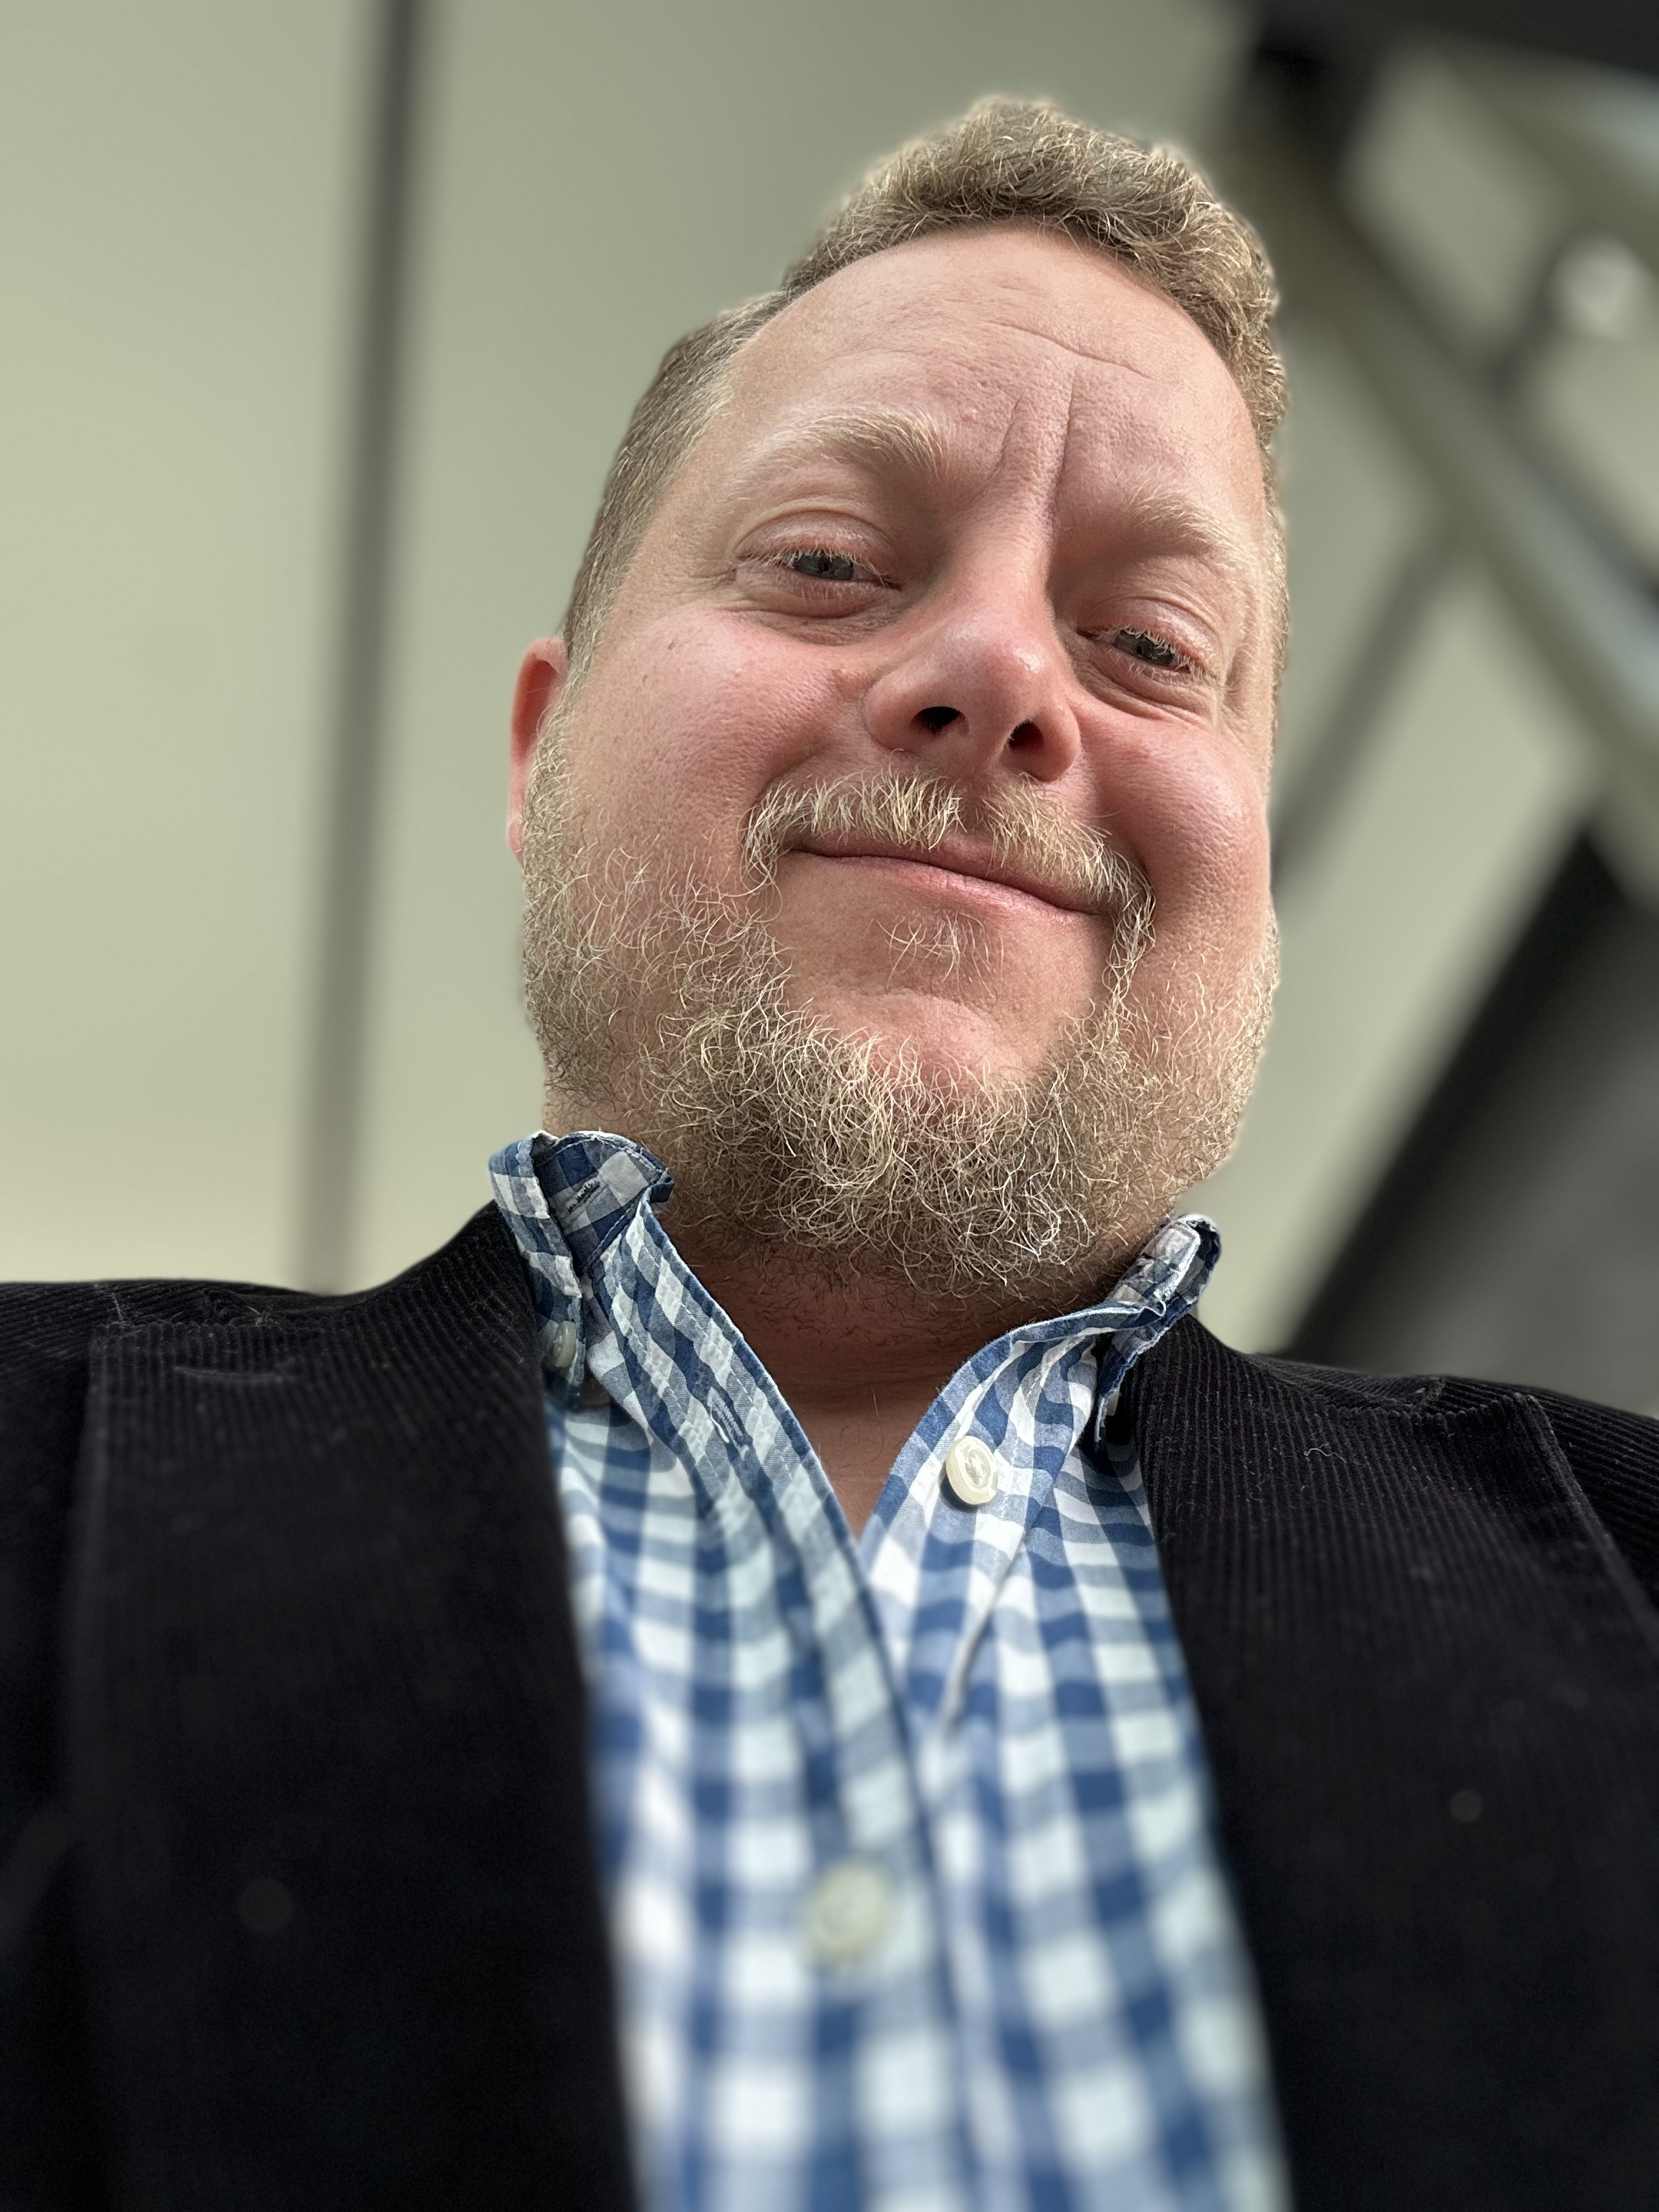
Andy Dyrcz — cybersecurity leader and author of The CISO Crucible

Andy Dyrcz is a cybersecurity leader and CISO who has spent his career at the uncomfortable intersection of risk, revenue, and human behavior.

Over the past decade, he has helped B2B SaaS companies build security programs that can withstand real-world pressure — from regulatory scrutiny and board expectations to production outages and late-night incident calls.

The CISO Crucible grew out of a simple realization: most security guidance tells leaders what they should do, but rarely shows what it feels like to do it while everything is on fire.

This is his first novel-length leadership story, but likely not his last.

Ready to Step Into the Crucible?

Get the Book

Available in paperback, ebook, and audiobook.